isavscan.xyz (.college, .christmas, .boats, .biz, ...)
I recently noticed some odd looking DNS failures logged by unbound, and thought the notes I made myself might be of use to others. I've refined them and reproduced them here.
TL;DR, this blog post describes what looks like scans for open DNS resolvers.
log entries
The initial log entries I noticed looked like this:
2025-11-11T19:58:23.525313+01:00 vps-1 unbound: [2139:0] info: 220.181.7.203 ltvzv.b069fe97.1.v4.isavscan.xyz. A IN SERVFAIL 0.345854 0 50
2025-11-10T16:33:23.578503+01:00 vps-1 unbound: [2139:0] info: 176.105.254.150 hupfw.b069fe97.0.v4.isavscan.xyz. A IN SERVFAIL 0.269942 0 50
2025-11-10T16:33:23.569348+01:00 vps-1 unbound: [2139:0] info: 220.181.7.203 jchzc.b069fe97.1.v4.isavscan.xyz. A IN SERVFAIL 0.271445 0 50
The first two labels of the FQDN aside, it was the combination of the source IP's and the hexadecimal label that caught my attention, especially the line where the source IP is 176.105.254.150, as it is adjacent to www.bogus.net. This IP, to my knowledge, is not in use -- thus very likely forged. The second label (b069fe97) is a hexadecimal representation of 176 105 254 151, the IP address of the unbound server.
I cannot know for sure if the other source IP (220.181.7.203) is forged; but there is a good chance that it is. The web server running on this host has a valid certificate for baidu.cn and will happily respond with a 302 redirect to www.baidu.com (abbreviated):
$ openssl s_client -connect 220.181.7.203:443
CONNECTED(00000003)
..
Certificate chain
0 s:C = CN, ST = \E5\8C\97\E4\BA\AC\E5\B8\82, O = "BeiJing Baidu Netcom Science Technology Co., Ltd", CN = www.baidu.cn
   i:C = US, O = "DigiCert, Inc.", CN = DigiCert Secure Site Pro G2 TLS CN RSA4096 SHA256 2022 CA1
   a:PKEY: rsaEncryption, 2048 (bit); sigalg: RSA-SHA256
   v:NotBefore: Feb 12 00:00:00 2025 GMT; NotAfter: Mar  3 23:59:59 2026 GMT
..
GET / HTTP/1.0
Host: baidu.cn

HTTP/1.0 302 Found
Location: https://www.baidu.com/
Date: Fri, 14 Nov 2025 21:29:26 GMT
Content-Length: 45
Content-Type: text/html; charset=utf-8

<a href="https://www.baidu.com/">Found</a>.

closed
But refuses to serve other forward names registered to it, such as 12555.com (ref. Censys):
$ openssl s_client -connect 220.181.7.203:443
CONNECTED(00000003)
..
GET / HTTP/1.0
Host: 12555.com

HTTP/1.0 403 Forbidden
Server: bfe
Date: Fri, 14 Nov 2025 22:01:03 GMT
Content-Length: 0
Content-Type: text/plain; charset=utf-8

closed
Later, I pulled out the rest of the available logs I had for this server and found that queries had been coming from similar domains since the end of December 2024.
..
2025-02-01T16:23:23.636855+01:00 vps-1 unbound: [424:0] info: 94.253.155.122 aecwk.b069fe97.1.v4.isavscan.baby. A IN SERVFAIL 0.230972 0 51
..
2025-01-01T15:58:42.916907+01:00 vps-1 unbound: [441:0] info: 176.105.254.150 stniu.b069fe97.0.v4.isavscan.click. A IN SERVFAIL 0.000000 0 52
..
2024-12-30T22:19:25.766984+01:00 vps-1 unbound: [441:0] info: 1.1.1.1 ohnmy.b069fe97.1.v4.isavscan.autos. A IN SERVFAIL 0.235094 0 52
2024-12-30T22:19:25.767968+01:00 vps-1 unbound: [441:0] info: 176.105.254.150 llhel.b069fe97.0.v4.isavscan.autos. A IN SERVFAIL 0.236228 0 52
In lieu of having packet captures, recent kernel log entries also provided clues that (some of/all?) the packets were forged (nothwithstanding the fact that some packets appeared to come from the "host next door") -- their TTL values were all over the place:
/var/log/kern.log.1:Nov 10 19:28:06 francine kernel: [8479931.486237] iptables denied: IN=eth0 OUT= MAC=00:1e:c9:df:e0:69:10:e3:76:13:8d:f4:08:00 SRC=220.181.7.203 DST=193.214.208.178 LEN=78 TOS=0x00 PREC=0x00 TTL=229 ID=54616 PROTO=UDP SPT=12345 DPT=53 LEN=58
/var/log/kern.log.1:Nov 10 20:22:36 katchoo kernel: [8482935.989515] iptables denied: IN=eth1 OUT= MAC=00:24:e8:2f:e6:29:10:e3:76:13:8d:f4:08:00 SRC=220.181.7.203 DST=193.214.208.179 LEN=78 TOS=0x00 PREC=0x00 TTL=220 ID=14339 PROTO=UDP SPT=12345 DPT=53 LEN=58
/var/log/kern.log.1:Nov 12 03:29:49 francine kernel: [8595229.031588] iptables denied: IN=eth0 OUT= MAC=00:1e:c9:df:e0:69:10:e3:76:13:8d:f4:08:00 SRC=220.181.7.203 DST=193.214.208.178 LEN=78 TOS=0x00 PREC=0x00 TTL=122 ID=42324 PROTO=UDP SPT=12345 DPT=53 LEN=58
/var/log/kern.log.1:Nov 12 05:50:55 katchoo kernel: [8603428.019975] iptables denied: IN=eth1 OUT= MAC=00:24:e8:2f:e6:29:10:e3:76:13:8d:f4:08:00 SRC=220.181.7.203 DST=193.214.208.179 LEN=78 TOS=0x00 PREC=0x00 TTL=192 ID=64672 PROTO=UDP SPT=12345 DPT=53 LEN=58
While I am at it, I will plug Gravwell Community Edition, which is what I use to process my logs. Its piped query language is nice, data does not need to be in pre-defined schemas on ingest and the free non-commercial license has a cap that's sensible for home/lab use (~14GB/day). I was also pleasantly surprised to find that Gravwell has no problems consuming Netflow/IPFIX records, such as those produced by softflowd.
other intel
There are other sources on the Internet with similar information. "JoshVogel0" on Palo Alto's LiveCommunity wrote in April 2025 that they had seen similar traffic. The day before I saw these in my log, "Gcoochey" responded that they had recently seen this too, always using source port 12345.
A Russian security blog entry dated "7 months ago" states that "several domains have been observed in scans using DNS tunneling techniques" (SEC-1275-1), listing isavscan in a number of TLD's, including .autos, .baby, .beauty, .biz, .bond, .cfd, .christmas, .click and .college. The blog also provides the nameserver for these domains (209.141.56.200 and 2605:6400:20:9d:2d8c:6f33:f4db:ab02), which have not changed since:
$ dig dead.babe.0.v4.isavscan.xyz +trace
..
v4.isavscan.xyz.        1799    IN      NS      ns4.isavscan.xyz.
$ host ns4.isavscan.xyz
ns4.isavscan.xyz has address 209.141.56.200
$ dig dead.babe.0.v6.isavscan.xyz +trace
..
v6.isavscan.xyz.        1799    IN      NS      ns6.isavscan.xyz.
$ host ns6.isavscan.xyz
ns6.isavscan.xyz has IPv6 address 2605:6400:20:9d:2d8c:6f33:f4db:ab02
These networks are owned by a budget VPS provider (FranTech).
suricata eve.log
By chance I had 180G of Suricata eve.json with data from 2020 that I almost had forgotten about, so decided to take a look for the domain there.
It looks like the first time isavscan.tld showed up in some form or another was late June 2024 using the .college suffix:
{"timestamp":"2024-06-27T02:48:05.223533+0200","flow_id":962655561279789,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"spxko.c1d6d0b2.1.v4.isavscan.college","rrtype":"A","tx_id":0}}
{"timestamp":"2024-07-03T05:27:11.945856+0200","flow_id":2115403548421824,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"tmmdn.c1d6d0b2.1.v4.isavscan.boats","rrtype":"A","tx_id":0}}
{"timestamp":"2024-07-24T21:31:22.849280+0200","flow_id":2115403841729920,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"pproi.c1d6d0b2.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2024-08-04T05:16:46.496497+0200","flow_id":2115404312777585,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"laxfv.c1d6d0b2.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2024-08-04T17:40:36.231288+0200","flow_id":458675142821752,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.179","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"laxfv.c1d6d0b3.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2024-08-10T04:38:17.853625+0200","flow_id":2115403775542905,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"xuejy.c1d6d0b2.1.v4.isavscan.click","rrtype":"A","tx_id":0}}
{"timestamp":"2024-09-03T11:48:13.059307+0200","flow_id":2115403922663339,"in_iface":"eth0","event_type":"dns","src_ip":"178.215.236.84","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"lyxvh.c1d6d0b2.1.v4.isavscan.boats","rrtype":"A","tx_id":0}}
{"timestamp":"2024-10-19T18:27:27.850882+0200","flow_id":1134484974992322,"in_iface":"eth0","event_type":"dns","src_ip":"39.156.66.10","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"ydtzn.c1d6d0b2.1.v4.isavscan.christmas","rrtype":"A","tx_id":0}}
{"timestamp":"2024-11-03T06:07:16.216719+0100","flow_id":1134481335668367,"in_iface":"eth0","event_type":"dns","src_ip":"39.156.66.10","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"yejrc.c1d6d0b2.1.v4.isavscan.biz","rrtype":"A","tx_id":0}}
{"timestamp":"2024-12-03T05:49:34.749461+0100","flow_id":1134483631665045,"in_iface":"eth0","event_type":"dns","src_ip":"39.156.66.10","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"pgdil.c1d6d0b2.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2025-01-03T05:58:29.634453+0100","flow_id":320161600351829,"in_iface":"eth0","event_type":"dns","src_ip":"1.1.1.1","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"knfem.c1d6d0b2.1.v4.isavscan.click","rrtype":"A","tx_id":0}}
{"timestamp":"2025-01-05T13:16:35.155276+0100","flow_id":127502414732940,"in_iface":"eth0","event_type":"dns","src_ip":"175.235.213.85","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"eyqro.c1d6d0b2.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2025-02-03T06:43:29.504634+0100","flow_id":1331759157457722,"in_iface":"eth0","event_type":"dns","src_ip":"111.251.134.74","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"idiko.c1d6d0b2.1.v4.isavscan.click","rrtype":"A","tx_id":0}}
{"timestamp":"2025-03-03T06:31:32.475547+0100","flow_id":408920593285531,"in_iface":"eth0","event_type":"dns","src_ip":"109.251.136.23","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"whdne.c1d6d0b2.1.v4.isavscan.boats","rrtype":"A","tx_id":0}}
{"timestamp":"2025-04-03T07:37:31.686006+0200","flow_id":1117054935201718,"in_iface":"eth0","event_type":"dns","src_ip":"159.39.142.173","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"aiqol.c1d6d0b2.1.v4.isavscan.college","rrtype":"A","tx_id":0}}
{"timestamp":"2025-05-03T08:34:13.281036+0200","flow_id":1531021504104908,"in_iface":"eth0","event_type":"dns","src_ip":"206.251.162.78","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"nkrtc.c1d6d0b2.1.v4.isavscan.boats","rrtype":"A","tx_id":0}}
{"timestamp":"2025-06-03T07:18:53.204391+0200","flow_id":2182318076534375,"in_iface":"eth0","event_type":"dns","src_ip":"215.221.103.224","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"yhjzw.c1d6d0b2.1.v4.isavscan.beauty","rrtype":"A","tx_id":0}}
{"timestamp":"2025-06-06T18:00:19.835641+0200","flow_id":1791796209500217,"in_iface":"eth0","event_type":"dns","src_ip":"119.29.52.7","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"njdbv.c1d6d0b2.1.v4.isavscan.xyz","rrtype":"A","tx_id":0}}
{"timestamp":"2025-07-03T07:05:40.456163+0200","flow_id":1390704230462947,"in_iface":"eth0","event_type":"dns","src_ip":"28.95.81.154","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"ocwlw.c1d6d0b2.1.v4.isavscan.xyz","rrtype":"A","tx_id":0}}
{"timestamp":"2025-11-10T19:28:06.492833+0100","flow_id":583070511432993,"in_iface":"eth0","event_type":"dns","src_ip":"220.181.7.203","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"jchzc.c1d6d0b2.1.v4.isavscan.xyz","rrtype":"A","tx_id":0}}
{"timestamp":"2025-11-12T03:29:49.589122+0100","flow_id":583071625510210,"in_iface":"eth0","event_type":"dns","src_ip":"220.181.7.203","src_port":12345,"dest_ip":"193.214.208.178","dest_port":53,"proto":"UDP","dns":{"type":"query","id":12345,"rrname":"ltvzv.c1d6d0b2.1.v4.isavscan.xyz","rrtype":"A","tx_id":0}}
end note / diagram
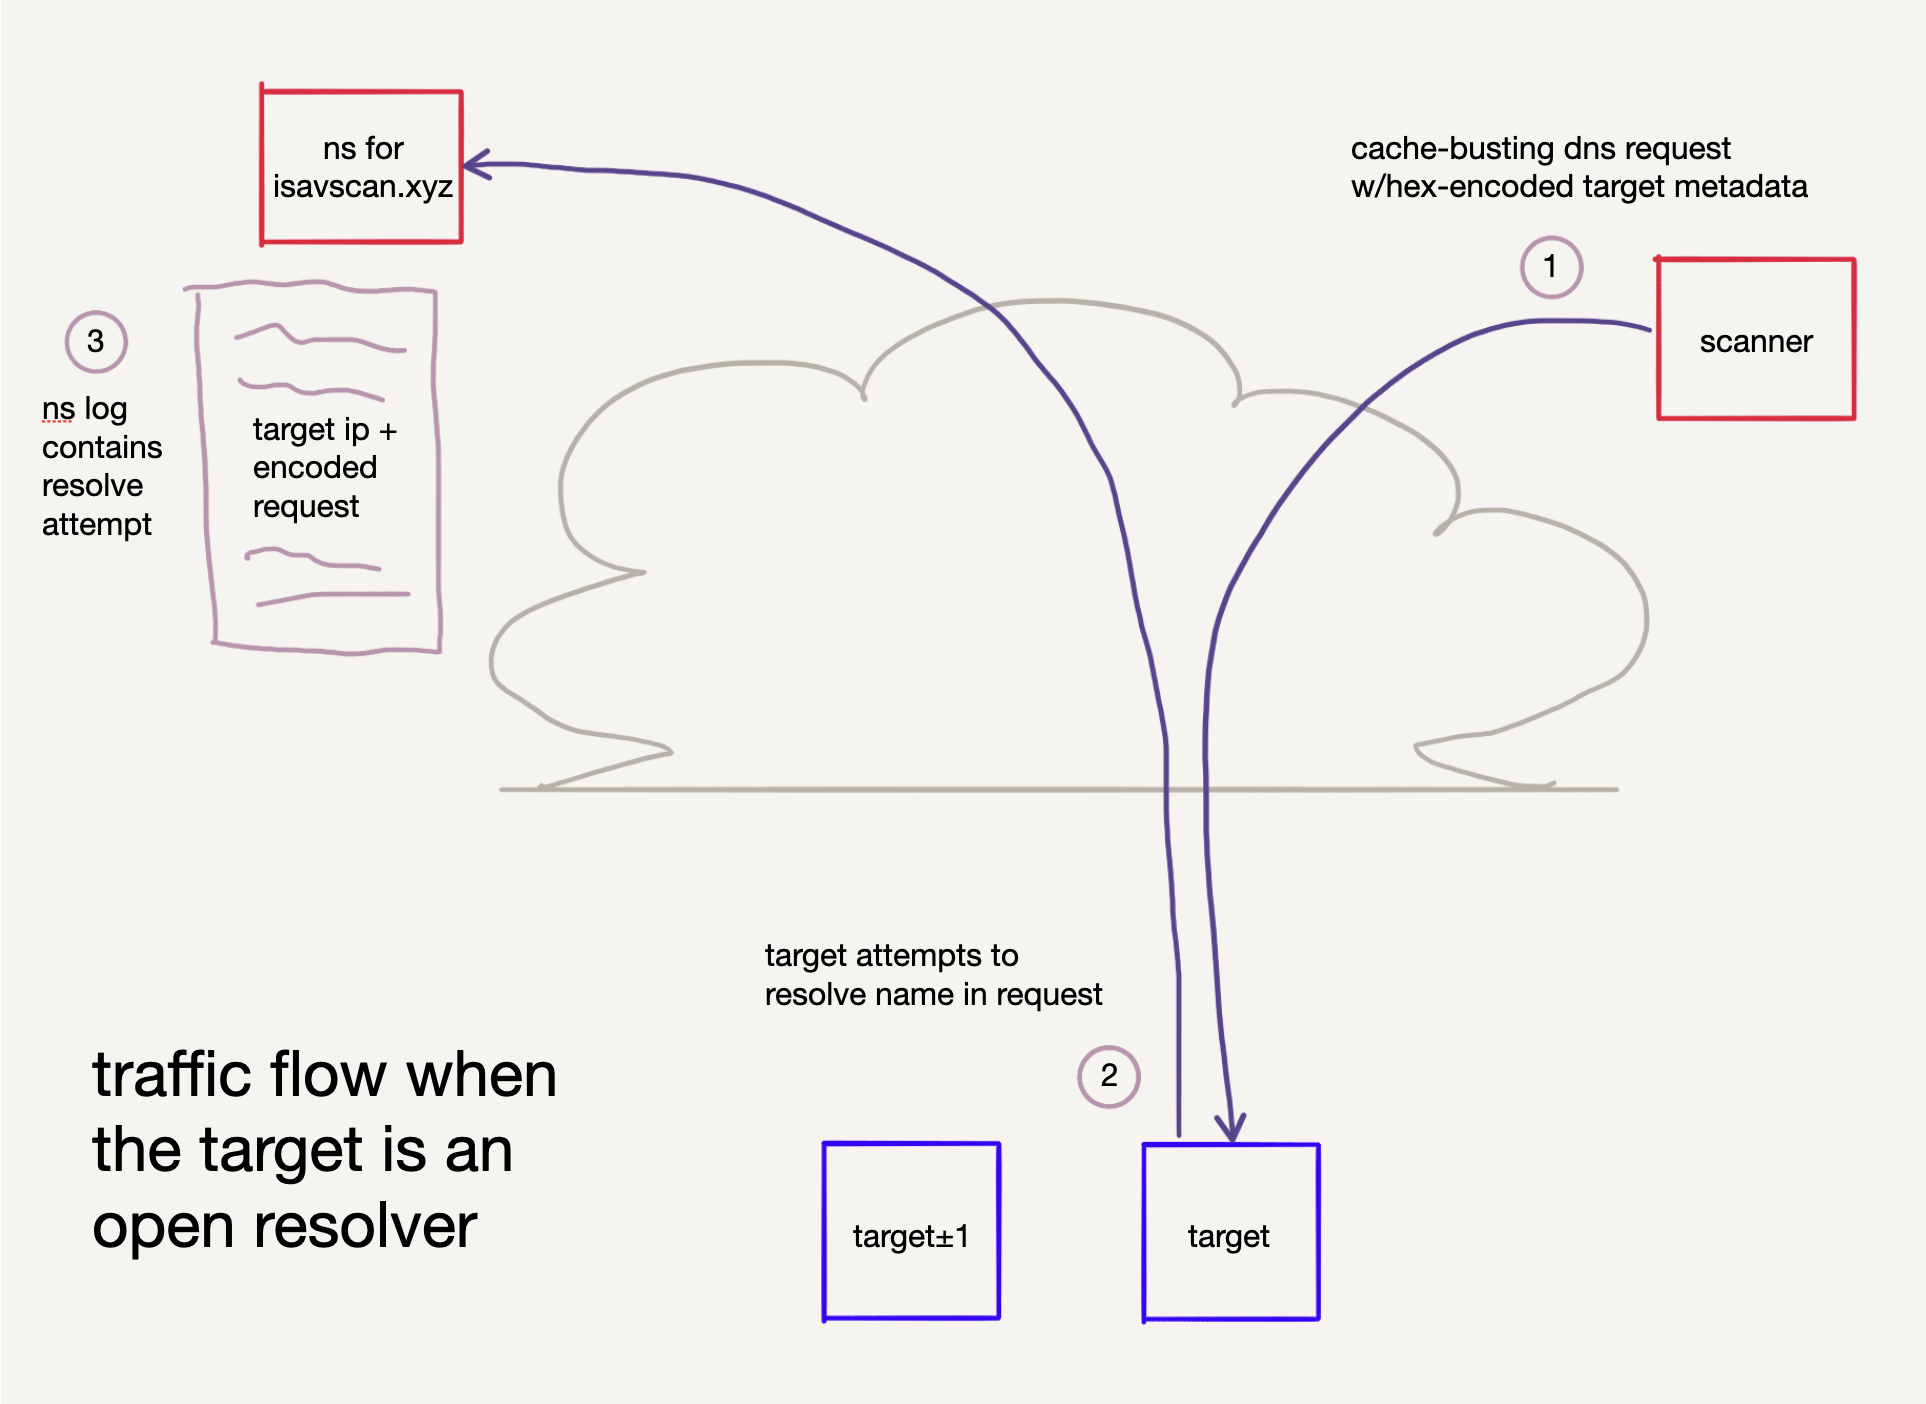
The way they form the (forged) DNS requests (1) borrows from DNS tunneling, in that they try to make sure that the spoofed request forces a DNS lookup (2) from the targeted host (if it is running an open resolver). This is achieved through unique host labels for each scan (e.g. yhjzw, njdbv, ocwlw, and so forth) such that there is no chance of a cache hit (cache hit = no upstream lookup).
The name server for the scanning domain logs the request (3), which includes the hex encoded target data and target IP address but does not respond to the request (at least not in this case, and there really is no need to generate extra traffic if all you want is to obtain a list of poorly configured DNS servers).
end end note
Here's a different way of encoding the target IP metainformation. My guess is that as long as there are (DDoS, cache poisoning, ..) attacks that can be performed using open resolvers, scans for them will occur.
It's normally quite easy to spot the difference between naughty and research. Here's someone probably not doing benign research, since everything needs to be questioned:
2025-11-08T06:02:57.640089+01:00 vps-1 unbound: [2139:0] info: 47.237.13.250 qcl1256l176l105l254l151l1031_batch_253l.ns5.48232025.xyz. A IN SERVFAIL 0.208673 0 74
$ dig dangao.ns5.48232025.xyz +trace
..
ns5.48232025.xyz.       60      IN      NS      ns5a.48232025.xyz.

$ host ns5a.48232025.xyz
ns5a.48232025.xyz has address 8.138.147.126

$ whois 8.138.147.126
..
inetnum:        8.128.0.0 - 8.159.255.255
netname:        ALICLOUD
descr:          Aliyun Computing Co.LTD
..

$ whois 47.237.13.250
..
NetHandle:      NET-47-235-0-0-1
Parent:         NET47 (NET-47-0-0-0-0)
Organization:   Alibaba Cloud LLC (AL-3)
..

$ host 47.237.13.250
Host 250.13.237.47.in-addr.arpa. not found: 3(NXDOMAIN)
While on the other hand, you have this where nothing is spoofed and everything is out in the open:
2025-11-07T01:27:26.891595+01:00 vps-1 unbound: [2139:0] info: 216.31.13.41 a2959736471p65522i8016.d202511070000026011.t50278.dnsresearch.cymru.com. A IN SERVFAIL 0.208764 0 89
$ host 216.31.13.41
41.13.31.216.in-addr.arpa domain name pointer serv93-as05-eth1-0.svcs.ord08.cymru.com.
